How to Enable UAC Administrator Display in Windows 11

This guide explains how to show or hide administrator accounts when a standard user triggers a security prompt in Windows 11. It covers the Local Security Policy, Group Policy and Registry methods, and says which Windows editions each one works on.
Press Win+R, type gpedit.msc, and press Enter. Go to Computer Configuration Administrative Templates Windows Components Credential User Interface, double-click Enumerate administrator accounts on elevation, select Enabled, then click Apply and OK. Restart your PC. On Home edition, use Registry Editor to navigate to 🗝️HKEY_LOCAL_MACHINE\
Understanding UAC Administrator Display in 🪟 Windows 11
The UAC administrator display setting controls whether Windows lists your local administrator accounts when a standard user hits a User Account Control (UAC) prompt, such as when installing software or changing a system setting. This setting helps you balance security and convenience.
Showing the accounts makes elevation faster, because the user picks an account from a list and types only a password. Hiding them is slightly more secure, because the user must type both the administrator’s username and password. Someone who doesn’t know the account names can’t just pick one from a list. On a typical Windows 11 PC the accounts are not listed unless you turn this on.
What happens when you are done? You will either see a list of available administrator accounts when a prompt appears, or you will have to enter the credentials by hand every time.
When to Use This
Pick the method that matches your edition of Windows 11:
- Windows 11 Pro, Enterprise or Education: Use the Group Policy method. The Local Security Policy tool is also available on these editions.
- Windows 11 Home: Use the Registry method. Home does not include the Group Policy Editor or the Local Security Policy tool.
A wrong edit can cause system errors, and a backup gives you an easy way back.
Method 1Using Local Security Policy (secpol.msc)
The Local Security Policy tool (secpol.msc) controls how UAC behaves when it asks for permission. It is available on Pro, Enterprise and Education only. Be aware that the policy below sets how the elevation prompt asks administrators to approve a change (consent or credentials). It does not control whether administrator accounts are listed. For the account list, use the Group Policy or Registry method in the next sections.
- Press Win + R, type
secpol.msc, and press Enter. If UAC asks for permission, approve it. The Local Security Policy window opens. - In the left pane, go to Local Policies Security Options A long list of security settings appears on the right.
- Scroll to User Account Control: Behavior of the elevation prompt for administrators in Admin Approval Mode.
- Double-click it. A properties window opens with a drop-down list.
- Choose the behavior you want, such as a consent prompt or a prompt for credentials, then click Apply and OK.
To undo the change, reopen the setting and pick the option it was set to before. The Windows default for administrators is a consent prompt for non-Windows binaries.
⚠️ Admin Privileges Required: You must be signed in as an administrator to modify these policies.
Method 2Using Group Policy Editor
The Group Policy Editor (gpedit.msc) is the standard way to decide whether administrator accounts are listed on the elevation prompt. It is available on Windows 11 Pro, Enterprise and Education. If Windows says it cannot find gpedit.msc, you are most likely on Home, so use the Registry method instead.
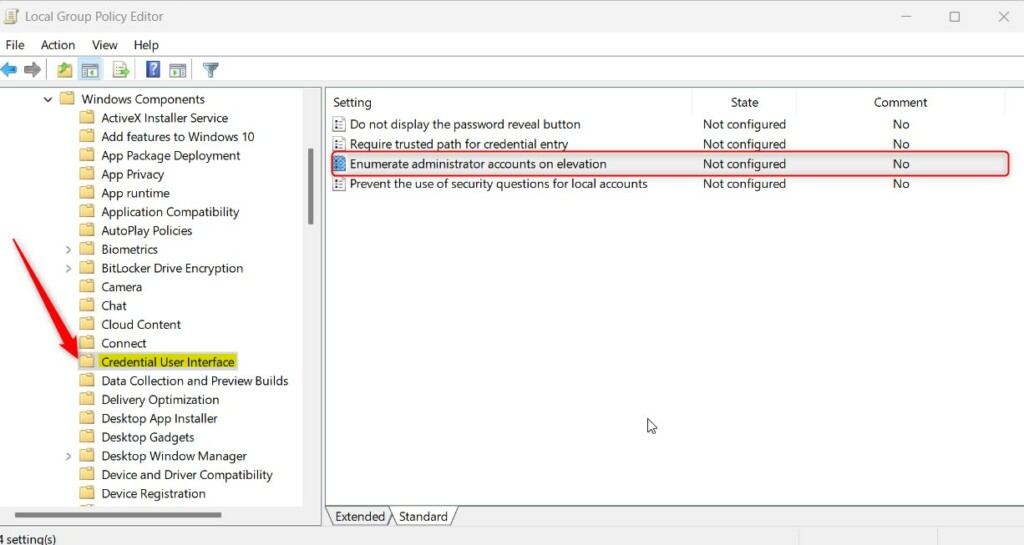
Follow these steps:
- Press Win + R, type
gpedit.msc, and press Enter. The Local Group Policy Editor opens. - In the left pane, go to Computer Configuration Administrative Templates Windows Components Credential User Interface The policy list appears on the right.
- Double-click Enumerate administrator accounts on elevation. A settings window opens, similar to the one below.
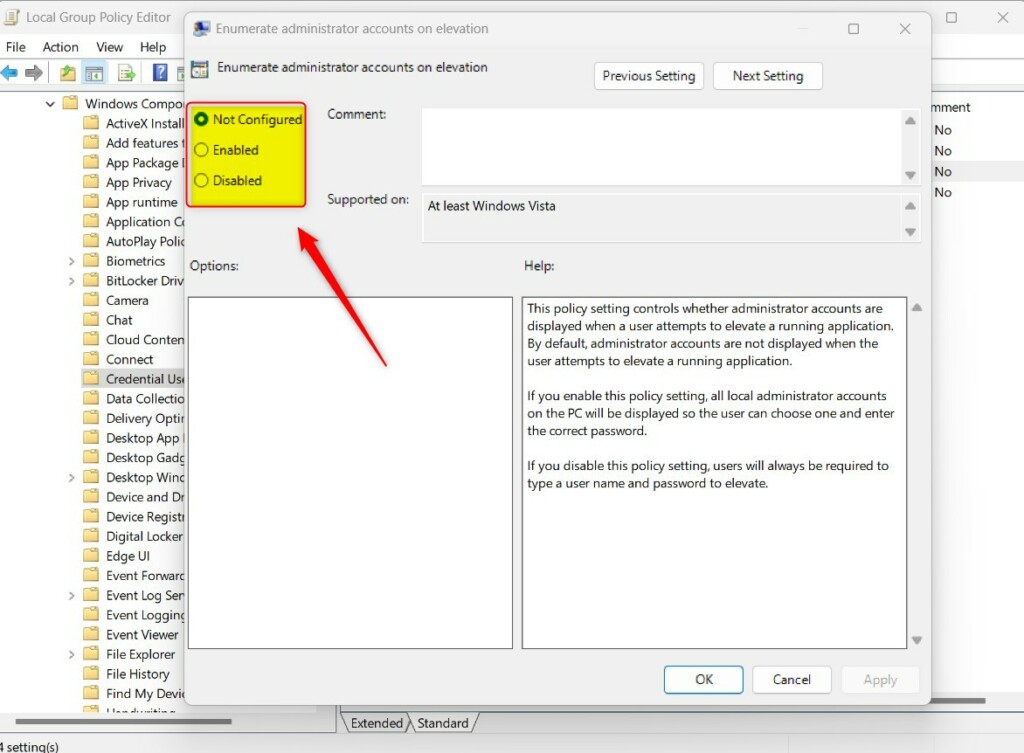
Display administrator accounts in the UAC prompt - Choose Enabled to show the accounts, or Disabled to hide them. Not Configured leaves Windows at its default, which is not to list them.
- Click Apply, then OK.
- Restart your PC so the change takes effect.
To undo the change, open the same policy, select Not Configured, click OK, and restart.
Method 3Using Windows Registry Editor
On Windows 11 Home, you can get the same result by editing the registry with regedit. You add one value that tells Windows whether to list administrator accounts on the prompt. The same method also works on Pro and Enterprise if you prefer it.
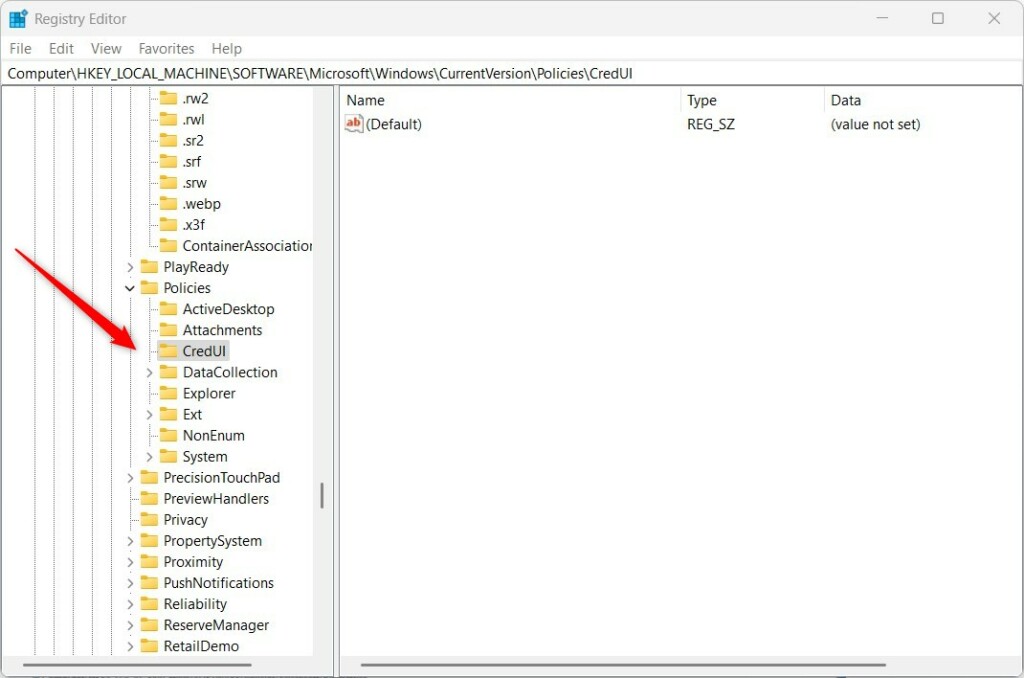
Follow these steps:
- Press Win + R, type
regedit, and press Enter. Approve the UAC prompt if it appears. The Registry Editor opens. - Go to
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\CredUI. You can paste the path into the address bar at the top of the editor. If the last key in the path does not exist, right-click its parent key, select New Key, and name it to match the path. - Right-click an empty area in the right pane and select New DWORD (32-bit) Value. A new value appears with its name highlighted for editing.
- Name it
EnumerateAdministratorsand press Enter.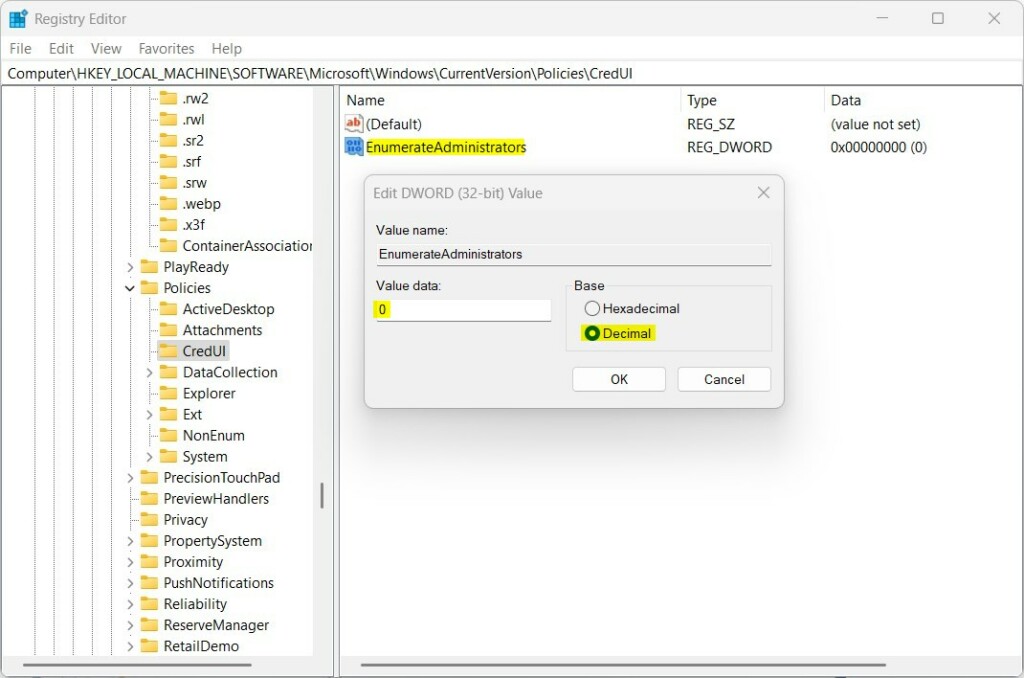
Display administrator accounts in the UAC prompt - Double-click the new value, enter 1 in the Value data box to show accounts or 0 to hide them, and click OK.
- Close the Registry Editor and restart your PC.
To undo the change, set the value to 0 or delete the value, then restart.
Change only the value described here, and back up first.
Security Risks and Best Practices
Disabling UAC prompts, or making administrator accounts visible, can make it easier for malware or an unauthorized user to get elevated access. Keep UAC enabled at the default level. If a shared PC has several administrator accounts, consider leaving the list hidden so the account names are not exposed to every user. For more information, visit the official Microsoft UAC documentation.
Summary
You can control how administrator accounts appear on UAC prompts in Windows 11 with the Group Policy Editor (Pro, Enterprise and Education) or the Registry (all editions, including Home). Restart your computer afterward so the change applies. Use the Local Security Policy tool when you want to change how UAC asks administrators for approval, but remember that it does not control the account list. Keep UAC enabled at all times.
Was this guide helpful?

About the Author
Richard
Tech Writer, IT Professional
Richard is a writer at Geek Rewind who turns complex IT tasks into clear, step-by-step guides. He draws on years of hands-on experience in system administration and enterprise IT operations, focusing on Windows, Linux and WordPress: the problems people actually run into, and the fixes that work. His server and WordPress guides come from systems he runs himself. Richard builds and maintains the platform behind Geek Rewind, from its Ubuntu servers and Nginx configuration to its custom WordPress plugins. Many new tutorials start with readers' questions, and he's always glad to answer them in the comments.
No comments yet — be the first to share your thoughts!