How to Allow Remote Connections to MySQL Database Server

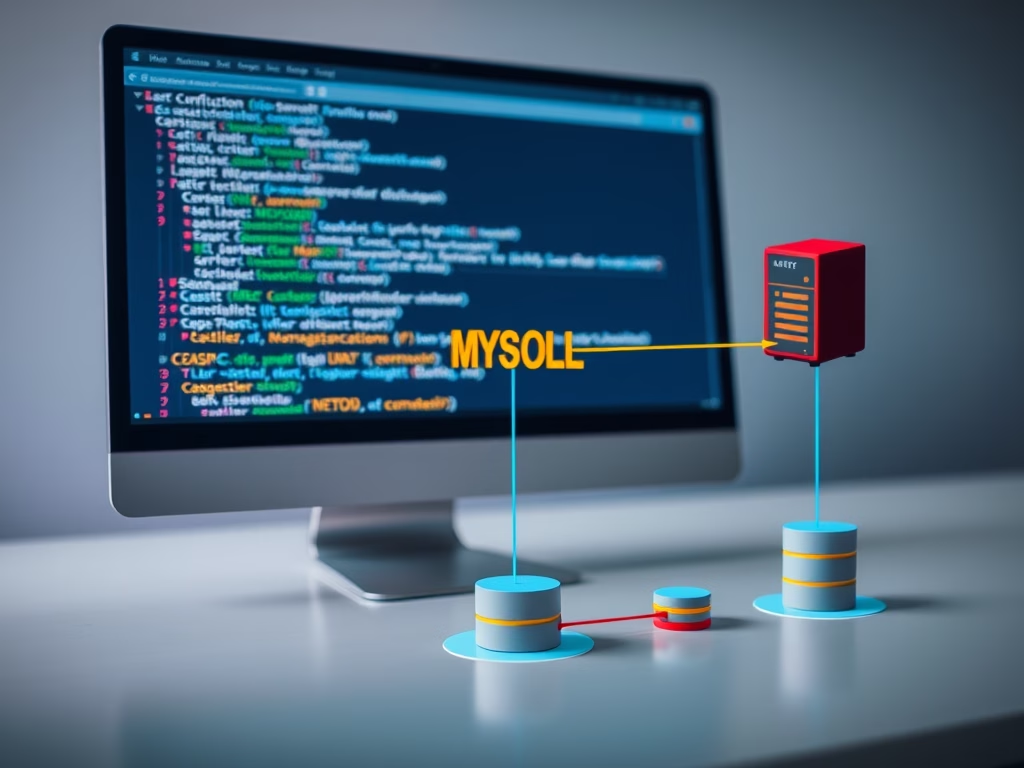
Remote connections to a MySQL database server let other computers on your network or the internet access your database instead of just the host machine. By default, MySQL blocks outside access and listens only to local requests on IP address 127.0.0.1 for security reasons.
You can open up access by changing the bind-address setting in your configuration file to 0.0.0.0 and updating your user permissions. Strong passwords help keep your data safe once other machines connect.
Edit your MySQL configuration file (e.g., `mysqld.cnf`) to change `bind-address` from `127.0.0.1` to `0.0.0.0` or your server’s IP. Restart MySQL, then grant remote user privileges using `CREATE USER` and `GRANT` statements.
Step 1Configure MySQL to Listen for Remote Connections
To accept remote connections, you need to change how MySQL listens for incoming traffic. Operating systems limit default listening scope to localhost, meaning the software only answers queries originating on the local machine.
MySQL only listens to requests from the local machine by default. Location of the configuration file depends on your operating system.
Configuration file paths vary by operating system distribution:
- Ubuntu/Debian:
/etc/mysql/mysql.conf.d/mysqld.cnf - Fedora/RHEL:
/etc/my.cnf
For Ubuntu or Debian users:
Open the settings file with a text editor:
sudo nano /etc/mysql/mysql.conf.d/mysqld.cnfLocate the bind-address parameter within the text:
bind-address = 127.0.0.1Modify the value to accept all incoming connections:
bind-address = 0.0.0.0Check for a skip-networking line next. Inserting a # character at the beginning disables that restriction:
# skip-networkingSave the changes and exit the editor.
For Fedora or RHEL users:
Open the settings file:
sudo nano /etc/my.cnfLocate or add the bind-address line beneath the [mysqld] section, assigning it a value of 0.0.0.0.
Step 2Restart MySQL
⚠️ Admin privileges required
For Ubuntu or Debian:
sudo systemctl restart mysqlFor Fedora or RHEL:
sudo systemctl restart mysqldStep 3Create a User for Remote Access
Once external network listening is enabled, create a dedicated database user account for remote authentication. Logging into the database shell allows executing queries that establish the username, allowed origin IP, and authentication credentials.
Log into MySQL as the root user:
sudo mysqlAuthenticate with an existing password instead:
mysql -uroot -pCreate a new user account while substituting placeholder values with actual details:
CREATE USER 'user_name'@'ip_address' IDENTIFIED BY 'user_password';Grant database privileges to the newly created account:
GRANT ALL ON database_name.* TO 'user_name'@'ip_address';Each placeholder serves a specific purpose in the command structure.
user_name= the name of the new userip_address= the IP address of the remote computer (use%to allow any IP)user_password= the password for this userdatabase_name= the database the user can access
Example:
Establishing an account named "john" connecting from IP 10.8.0.5 with password "secure123" targeting the "sales_db" database follows this syntax:
CREATE USER 'john'@'192.168.0.1' IDENTIFIED BY 'secure123';
GRANT ALL ON sales_db.* TO 'john'@'192.168.0.1';
Step 4Open the Firewall
⚠️ Admin privileges required
Port 3306 handles database communication. Operating system firewalls require explicit rules allowing traffic on this port, though specific commands vary by utility.
For UFW (Ubuntu):
Permit access from a designated IP address:
sudo ufw allow from 192.168.0.1 to any port 3306Allowing connections from any IP remains insecure:
sudo ufw allow 3306/tcpFor iptables:
Permit access from a designated IP address:
sudo iptables -A INPUT -s 192.168.0.1 -p tcp --destination-port 3306 -j ACCEPTAllowing connections from any IP remains insecure:
sudo iptables -A INPUT -p tcp --destination-port 3306 -j ACCEPTFor FirewallD (Fedora/RHEL):
Establish a dedicated network zone for database communication:
sudo firewall-cmd --new-zone=mysqlzone --permanent
sudo firewall-cmd --reload
sudo firewall-cmd --permanent --zone=mysqlzone --add-source=192.168.0.1/32
sudo firewall-cmd --permanent --zone=mysqlzone --add-port=3306/tcp
sudo firewall-cmd --reload
Allowing connections from any IP remains insecure:
sudo firewall-cmd --permanent --zone=public --add-port=3306/tcp
sudo firewall-cmd --reload
Step 5Test Your Connection
Test connectivity from the remote workstation:
mysql -u john -h 192.168.0.1 -pSubstitute john with the target username and 192.168.0.1 with the server address, providing the password when prompted.
Troubleshooting
Troubleshooting remote connections uncovers common hurdles like 'Can't connect to MySQL server' and 'Host is not allowed to connect.' Firewall blocks or misconfigured network listeners trigger connection failures, while permission mismatches cause host rejection errors.
Potential root causes include:
- Port 3306 is blocked by the firewall
- MySQL is not listening on the right IP address
Error: "Host is not allowed to connect"
User permissions lack authorization for the originating client IP address. Confirming account creation parameters resolves the mismatch.
Summary
Enabling remote MySQL access involves editing configuration files to set bind-address to 0.0.0.0, restarting the MySQL service, creating scoped user accounts, and opening firewall port 3306.
- Edit the MySQL config file and change
bind-addressto0.0.0.0 - Restart the MySQL service
- Create a new MySQL user with a specific IP address
- Give that user permission to access your database
- Open port 3306 in your firewall
- Test the connection from the remote computer
Administrative rights govern all configuration procedures. Verifying IP bindings and firewall rule sets resolves unexpected connection drops.
Was this guide helpful?
0% of readers found this helpful (1 votes)

About the Author
Richard
Tech Writer, IT Professional
Richard, a writer for Geek Rewind, is a tech enthusiast who loves breaking down complex IT topics into simple, easy-to-understand ideas. With years of hands-on experience in system administration and enterprise IT operations, he’s developed a knack for offering practical tips and solutions. Richard aims to make technology more accessible and actionable. He's deeply committed to the Geek Rewind community, always ready to answer questions and engage in discussions.
No comments yet — be the first to share your thoughts!